OWASP Top 10 Web Application Security Risks Explained for Developers
 Althaf Mohamed

Introduction to Web Application Security
In modern web engineering, security can no longer be treated as an afterthought or relegated to a pre-release audit. The Open Worldwide Application Security Project (OWASP) Top 10 represents a globally recognized awareness document for developers and web application security teams. It provides an authoritative overview of the most critical security risks threatening web applications today.
Understanding these vulnerabilities is essential for designing resilient distributed systems, writing secure serverless microservices, and defending sensitive user data against adversarial exploitation. In this guide, we break down the most prominent OWASP risks with practical engineering remediation techniques.
1. Broken Access Control
Broken Access Control occurs when users can act outside of their intended permissions. This is currently recognized by OWASP as the number one security risk in web applications. Examples include unauthorized record access via parameter tampering, elevating administrative privileges, and manipulating metadata or tokens.
Common Attack Scenario: Insecure Direct Object References (IDOR)
Consider an endpoint where a user requests their invoice details:
GET /api/invoices?id=1024If the backend server queries the database solely by id without verifying that the authenticated session owner matches the account that owns invoice 1024, any logged-in user can increment the ID and view arbitrary confidential customer invoices.
Defensive Implementation
Always enforce server-side ownership validation and implement Role-Based Access Control (RBAC) or Attribute-Based Access Control (ABAC):
// Secure implementation example in Node.js / Express
async function getInvoice(req, res) {
  const { id } = req.params;
  const currentUserId = req.user.id;

  const invoice = await db.invoices.findUnique({
    where: { id: String(id) }
  });

  if (!invoice || invoice.userId !== currentUserId) {
    return res.status(403).json({ error: "Access Denied" });
  }

  return res.json(invoice);
}
2. Cryptographic Failures
Formerly categorized as Sensitive Data Exposure, cryptographic failures occur when sensitive data—such as passwords, credit card numbers, health records, and API tokens—is transmitted in cleartext or stored using obsolete encryption algorithms (such as MD5 or SHA-1).
Remediation Checklist:
- Enforce TLS 1.3 across all endpoints with HTTP Strict Transport Security (HSTS).
- Hash passwords using adaptive algorithms like bcrypt, Argon2, or PBKDF2 with robust salt rounds.
- Never hardcode encryption secrets or keys in Git repositories; utilize secure secret managers (e.g., AWS Secrets Manager, Google Cloud Secret Manager).
- Disable caching on HTTP responses containing personally identifiable information (PII).
3. Injection Flaws (SQL, NoSQL, and Command Injection)
Injection flaws occur when untrusted user input is directly concatenated into a system interpreter or query engine without validation or escaping. While SQL injection remains prevalent, modern web stacks are also susceptible to NoSQL injection and OS command injection.
The golden rule for preventing injection is separating data from code execution through parameterized queries, object-relational mappers (ORMs), and strict input validation schemas.
4. Insecure Design
Insecure design represents a category focusing on flaws in architectural design and business logic rather than mere implementation bugs. A code implementation may be technically bug-free according to specification, yet inherently vulnerable because threat modeling was absent during initial design.
For example, a password reset flow that lacks rate limiting or allows infinite reset attempts creates an architectural vulnerability that enables credential stuffing and denial of wallet attacks.
5. Security Misconfiguration
Security misconfiguration is among the most frequently encountered vulnerabilities in cloud-native applications. It encompasses:
- Leaving default administrative accounts, passwords, and ports enabled.
- Exposing detailed stack traces, environment variables, or debug error logs to end users.
- Misconfigured Cross-Origin Resource Sharing (CORS) headers allowing wildcard origins on authenticated endpoints.
- Running unnecessary server features, sample pages, or unpatched legacy libraries.
6. Vulnerable and Outdated Components
Modern applications are constructed using hundreds of open-source third-party dependencies. If your application depends on a library with known Common Vulnerabilities and Exposures (CVEs), an attacker can easily leverage automated scanners to identify and compromise your server.
Regularly run automated dependency security audits using tooling such as npm audit, Snyk, or GitHub Dependabot, and pin your software versions deterministically.
Conclusion & Best Practices
Securing web applications requires defense in depth. By adopting safe coding practices, enforcing strict authentication boundaries, practicing threat modeling during architectural planning, and monitoring systems with centralized logging, development teams can substantially mitigate the risks identified in the OWASP Top 10.
Frequently Asked Questions
Althaf Mohamed
Technical Author
Software Engineer and technical author specializing in web architectures, databases, and secure distributed systems.
Trending Now
Recent Posts
Beginner's Guide to Software Development: Everything You Need to Know in 2026
May 30, 2026
TypeScript vs JavaScript - Key Differences
May 04, 2026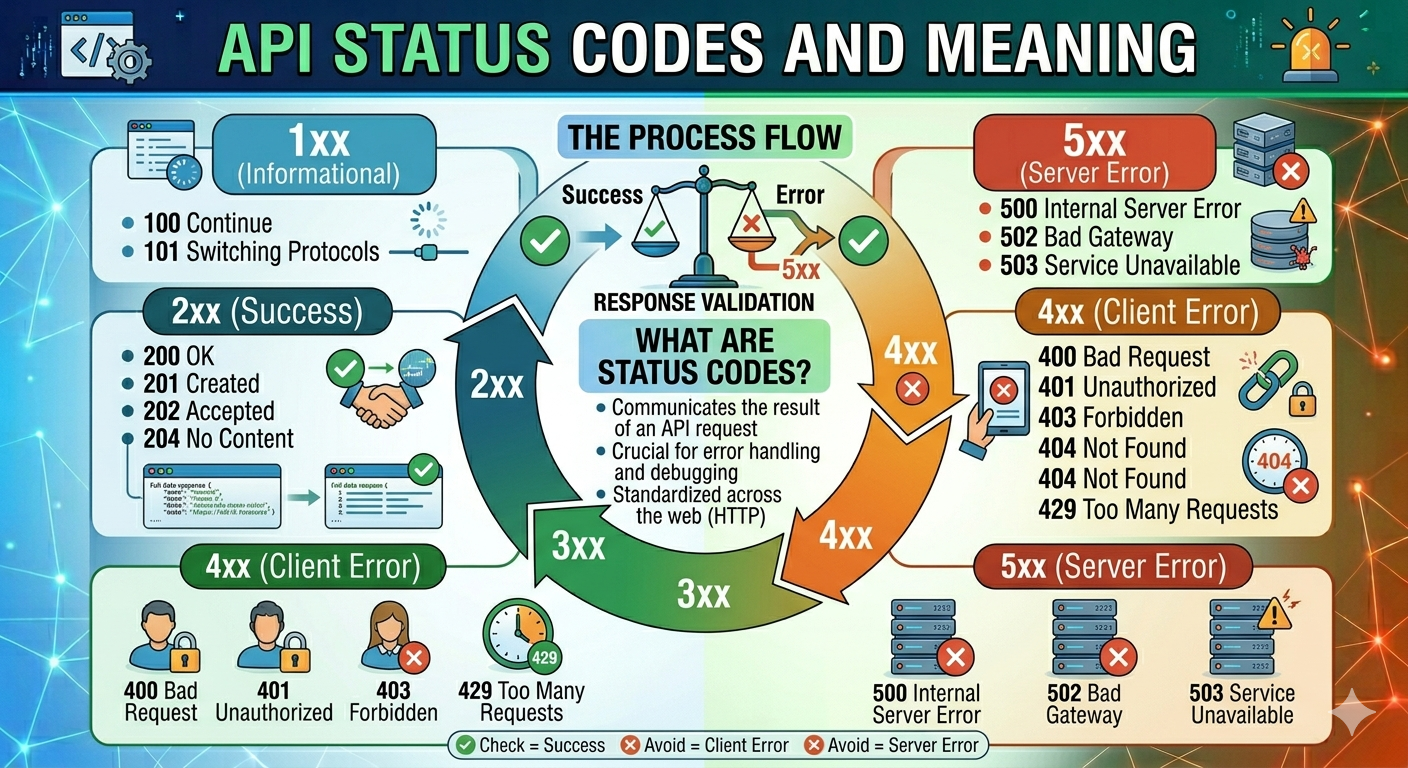
API Status Codes & Meanings
May 04, 2026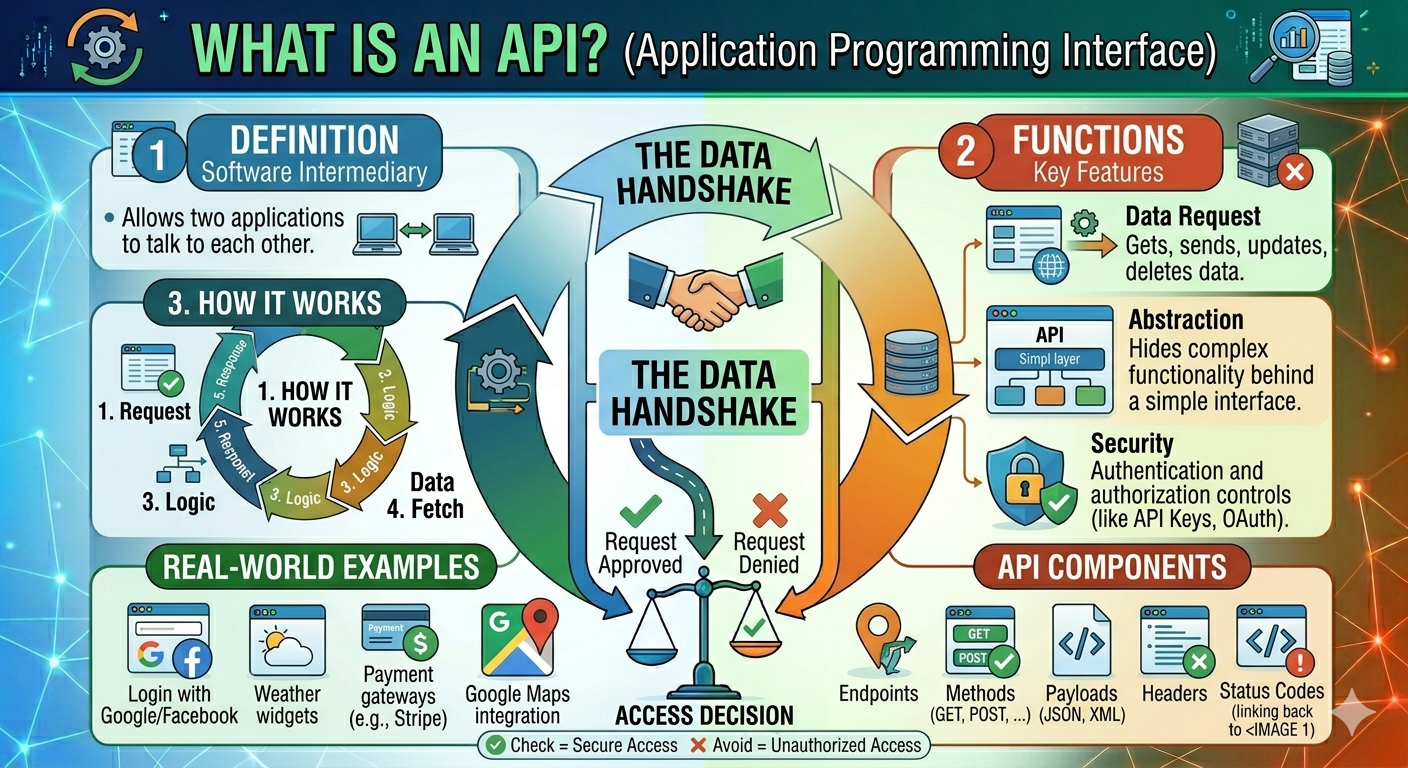
What is an Application Programming Interface (API)
May 04, 2026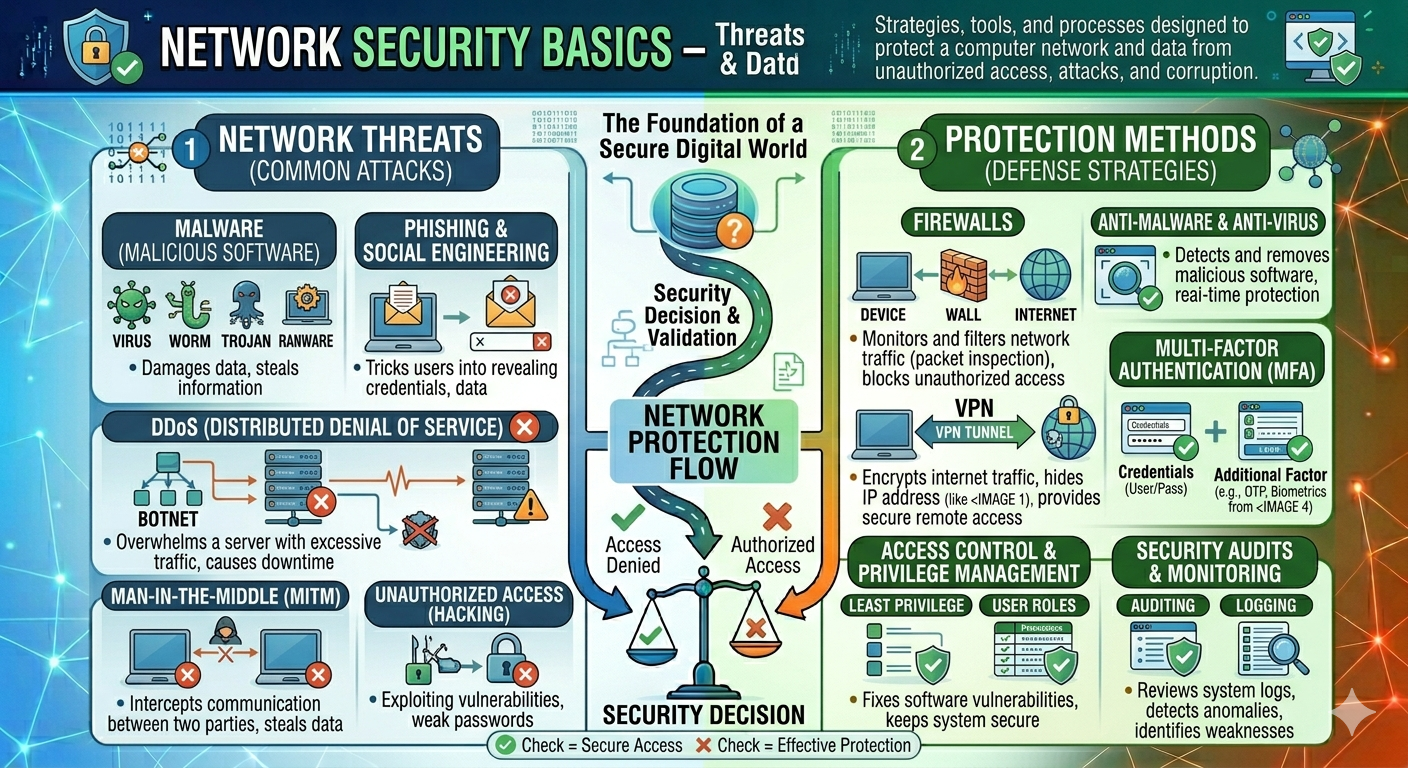
Network Security Basics – Threats & Protection Methods
May 04, 2026